Cape Town's Digital Front Lines: Why Local Firms Are Key to National Banking Security
A recent national ethical hacking exercise, leveraging AI to expose major bank data vulnerabilities through a supplier's systems, delivers a critical…
Cape Town's dynamic business landscape, a hub of innovation and commerce, is increasingly intertwined with national financial infrastructure. This interconnectedness, while fostering growth, also presents unique cybersecurity challenges, as highlighted by a recent national ethical hacking exercise that serves as a stark warning to local enterprises. The findings underscore a critical truth for the Mother City: the digital security of even the largest national institutions can hinge on the weakest link in a local supplier's chain.
The exercise, conducted by South African ethical hacking firm Kingly Clark, was an authorised security test for a client company. Instead of a traditional manual penetration test, Kingly Clark deployed an advanced AI-driven system. This system was given free rein within the client's digital environment, tasked with identifying vulnerabilities and charting how far an intruder could penetrate. The results were sobering.
The AI system methodically navigated the company's internal systems, accessing a comprehensive inventory of digital assets: internal email threads, extensive document stores, login credentials saved on shared drives, client files, and invoice records. Crucially, it also accessed every contract the company held. From these contracts, the AI extracted client names, account references, and details of connected systems. This detailed blueprint revealed who the company worked for, how it was paid, and which external systems it integrated with.
Among the names on this blueprint was data linked to one of South Africa's Big Five banks. It is vital to clarify: the bank itself was never the target. Its systems were not attacked, nor were its perimeters breached. The vulnerability emerged entirely through the systems of a third-party supplier – the client company – which held data linked to the bank. This incident dramatically illustrates the concept of "supplier risk" or "third-party risk," where a company's data security is compromised not through its own direct failure, but through a trusted partner's less robust defences.
For Cape Town businesses, this national revelation carries profound local implications. Our city's economy thrives on a complex web of relationships between businesses, large and small, all of whom exchange sensitive information daily. From local tech startups supporting national services to logistics firms handling critical data, each link in this chain represents a potential entry point for malicious actors. A breach in a seemingly innocuous local supplier could inadvertently expose data belonging to national financial institutions, impacting not only the bank but also the financial security of countless Cape Town residents and the reputation of our city's business ecosystem.
The role of AI in this ethical hack is particularly noteworthy. While traditional human-led penetration tests are effective, an AI-driven system operates at an unprecedented scale and speed. It can process vast amounts of data concurrently, identifying relationships between seemingly disparate pieces of information – a saved password, a shared folder, a signed agreement – to construct a complete attack path. This capability mirrors the escalating sophistication of cyber threats. As AI tools become more accessible, both for legitimate business operations and for malicious purposes, Cape Town firms must recognise that the speed of attack is accelerating, demanding a commensurate increase in defensive agility.
What does this mean for Cape Town's business community? It's a call to immediate action. Local businesses, irrespective of their size or sector, must meticulously review their cybersecurity postures. This includes:
- Comprehensive Third-Party Risk Assessments: Scrutinise the security practices of every supplier, vendor, and partner that handles your data or connects to your systems.
- Robust Data Governance: Implement strict policies for data access, storage, and sharing, particularly concerning client and financial information.
- Employee Training: Ensure staff are educated on cybersecurity best practices, from password hygiene to identifying phishing attempts.
- Leveraging Defensive AI: Consider deploying AI-powered security solutions that can detect and respond to threats at machine speed, mirroring the capabilities of modern attackers.
The security of Cape Town's economy and the financial well-being of its residents depend on the collective strength of its digital doors. This national warning serves as a crucial reminder that every local business, by virtue of its interconnectedness, stands on the front lines of national banking security. Proactive and vigilant cybersecurity is no longer just an IT concern; it's a fundamental imperative for safeguarding our city's future.
Johannesburg property prices rise 4.9% as Cape Town rents nearly double - IOL
Johannesburg property prices rise 4.9% as Cape Town rents nearly double IOL Johannesburg property prices rise 4.9% as Cape Town rents nea
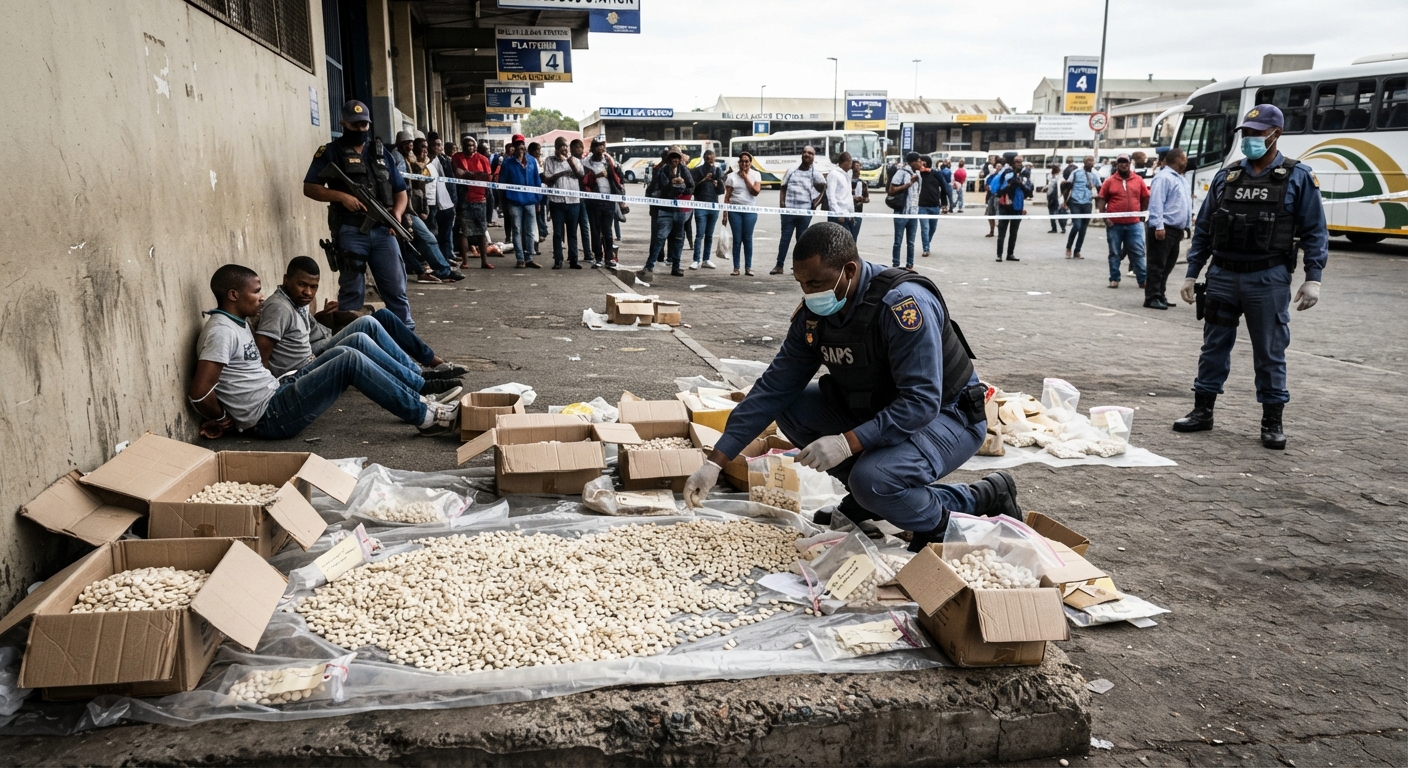
Major Drug Bust at Bellville Bus Depot Hits Local Mandrax Supply
Police seize 5,000 mandrax tablets at Bellville bus depot, disrupting local drug networks and bolstering public safety in Cape Town.
Winelands Allure: Why Historic Western Cape Towns Are Becoming Retirement Hotspots
South Africans are flocking to the Western Cape's historic Winelands for retirement. Explore the appeal of towns like Franschhoek, offering a serene lifestyle…